
DNS: the first milliseconds of a visit
Before opening a connection, the browser has to locate the service. Understanding resolution, caching, TTL and DNSSEC prevents delays and poorly planned changes.
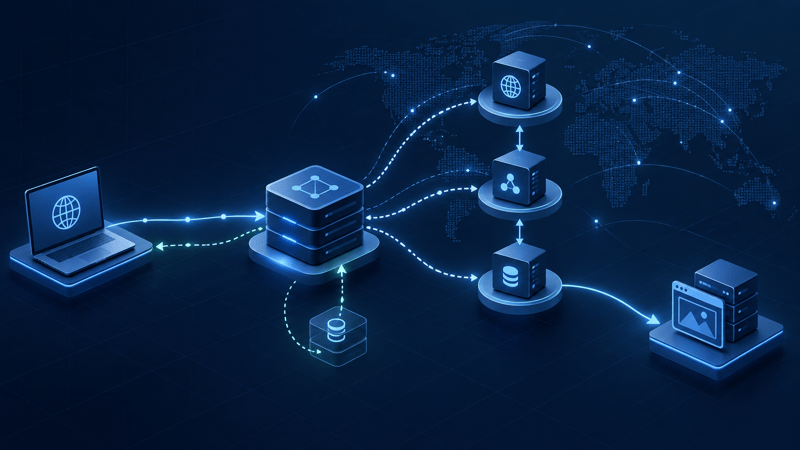
The stage before the connection
When someone opens an address, the browser does not yet know which network destination to contact. It asks the Domain Name System, or DNS, to turn a human-readable name into records that can be used to establish a connection. Until that answer arrives, the page transfer has not even started.
DNS time may look small in isolation, but it sits on the critical path of a first visit. If the answer is already cached, resolution can be almost immediate. If the resolver needs to walk the complete chain, every query, failure and additional attempt adds to the delay a visitor perceives.
Who actually answers the question
A query normally begins at a recursive resolver. It checks its own cache and, when no valid answer is available, follows the referrals needed to reach the authoritative server for the zone. Root and top-level domain servers generally do not know the final address of the website. They indicate which server is responsible for the next part of the answer.
This separation distributes responsibility and allows DNS to work at a global scale. It also explains why troubleshooting needs to examine the complete chain. Incorrect delegation, unavailable authoritative servers or inconsistent records can cause delays and failures that never appear in application code.
TTL is a freshness policy
A record can state how long an answer may be reused. That value, the TTL, counts inside each resolver from the moment it receives the answer, not on a clock shared by all of them.
A high TTL reduces queries and gives stability to records that change rarely. A low TTL shortens the life of stale information but increases query frequency. Before a planned migration, the reduction needs to happen early enough for previously cached values to expire. Lowering the TTL only when the change begins does not alter answers already stored under the former value.
Negative caching matters too. An answer saying that a name does not exist can remain cached for a period of time. Creating the record immediately after a failed lookup leaves part of the resolvers answering from the negative cache until that period ends.
Anycast distributes the delivery of a zone
On an Anycast network, the same service address can be announced from multiple locations. Routing sends the query to an instance that is reachable according to the network view. This reduces distance and distributes failures while keeping whatever the zone publishes: a configuration error is distributed along with it.
Real redundancy requires consistent authoritative servers, correct delegation and routes independent enough that one failure does not remove every answer. Anycast delivers; operating the zone defines what gets delivered.
DNSSEC protects authenticity, not secrecy
DNSSEC adds signatures that let resolvers validate the origin and integrity of received data. It helps detect forged answers when the chain of trust is complete. The query stays visible on the network: transport confidentiality is a separate subject, handled by DNS over TLS or over HTTPS.
Signing also introduces operational work. Keys, delegation records and validity periods need to remain synchronized. A broken chain can make an existing zone appear invalid to resolvers that perform DNSSEC validation.
A DNS change needs a runbook
Before changing a zone, record its current state, validate the new configuration through more than one resolver and plan a rollback. After the change, verify the authoritative answer, delegation, TTL, signatures where present and behavior across different networks.
DNS rarely attracts attention when it works. Yet it determines where every connection begins. Treating names, caches and delegation as architecture prevents a seemingly small change from becoming an outage that is difficult to explain.